Yes, your POS falls under UK GDPR. Every till, terminal and loyalty scanner that touches a customer’s name, card token or contact details is processing personal data, and the Data Protection Act 2018 applies whether you run one café or twelve shops. Start with four things: identify your lawful basis for each type of processing, confirm your system uses TLS 1.2+ with encryption at rest, keep a simple record of what data you hold, and check whether you need to register with the ICO.
TL;DR:
- Retailers must identify and document the lawful basis for each POS processing activity, such as payments, loyalty, or marketing, to ensure GDPR compliance.
- POS systems handling customer data need TLS 1.2+ encryption and encryption at rest; failure to confirm this indicates a security risk.
- Regularly review and delete data like loyalty records, CCTV footage, and receipts once they are no longer needed to minimize risks.
- Register with the ICO and pay the correct data protection fee, which most small retailers qualify for based on their processing volume.
- Staff must be briefed on data handling procedures, breach response, and customer rights, with proper access controls and routine checks to prevent breaches.
Table of Contents
- Quick GDPR for POS compliance checklist: five actions to start now
- What data do POS systems collect and why it matters
- Lawful basis and customer rights: matching POS tasks to legal grounds
- Technical and organisational measures your POS should demand
- Practical processes: records, retention, and ICO fees
- If POS data is breached: your incident response checklist
- When does a POS project need a DPIA?
- Making GDPR part of everyday POS operations
- How Switch-and-save helps you manage GDPR obligations at the till
- Sources
- FAQ
Quick GDPR for POS compliance checklist: five actions to start now
You don’t need a legal department to make progress this week. Work through these five steps in order, and brief your team as you go.
- Decide your lawful basis for each processing activity (payments, loyalty, marketing) and write it down, even in a spreadsheet.
- Confirm TLS 1.2+ and encryption at rest with your POS provider. If they can’t confirm this, that’s a red flag.
- Set retention limits for receipts, loyalty records and CCTV footage. Don’t keep data “just in case.”
- Check your ICO registration and confirm you’re paying the correct data protection fee tier.
- Brief staff on subject access requests, breach reporting, and who’s allowed to view customer records.
Pro Tip: Print this list and stick it near the till. Small errors add up, and most breaches start with a staff member who genuinely didn’t know the rule existed.
What data do POS systems collect and why it matters
A modern POS collects more than most owners realise, and each field carries a different level of risk. Basic transaction data (item, price, time) rarely identifies anyone. Once you add a name, phone number, or delivery address, you’re handling personal data in point of sale under UK GDPR — and the same rules apply whether that data sits in a till receipt or a loyalty app.
Common fields include:
- Customer name and contact details (email, phone)
- Delivery or billing address for online or click-and-collect orders
- Purchase history and loyalty scheme identifiers
- Limited payment tokens (never full card numbers, if your terminal is PCI compliant)
- CCTV footage covering the till area or shop floor
Full card numbers, home addresses and CCTV are higher-risk categories. Treat them with tighter access controls and shorter retention than a loyalty points balance. Data minimisation means only collecting what the transaction actually needs. Purpose limitation means you can’t quietly reuse loyalty data for a marketing campaign nobody agreed to.
Lawful basis and customer rights: matching POS tasks to legal grounds
Not every POS activity needs the same legal justification, and getting this wrong is one of the more common mistakes among smaller retailers. Payments and order fulfilment usually rest on contract (you need the data to complete the sale) or legal obligation (tax and accounting records). Fraud prevention and basic sales analytics typically fall under legitimate interests, provided you’ve run a balancing test weighing your business need against the customer’s privacy.
Marketing is different. Sending promotional emails or SMS through your POS’s loyalty features generally needs explicit consent, and this sits alongside the Privacy and Electronic Communications Regulations (PECR), which govern electronic marketing separately from GDPR itself. A customer who buys a coffee hasn’t automatically agreed to a newsletter.
Practical steps for managing this:
- Log which lawful basis applies to each POS function in your records of processing
- Give customers a clear, unticked opt-in box for marketing at the till or online checkout
- Build a simple process for handling access, rectification, erasure, and objection requests
- Note that under UK GDPR, individuals have eight distinct rights, and your POS provider should be able to help you locate a customer’s full record when asked
Technical and organisational measures your POS should demand
The ICO’s security principle sets a clear technical bar, and it’s one every POS provider should meet without you having to ask twice. Encryption in transit means TLS 1.2 or higher for any networked connection between your till, card terminal and cloud dashboard. Encryption at rest applies to anything stored, whether that’s a customer database or an overnight backup.
Beyond encryption, look for technical-control checklists:
- Role-based access so a part-time cashier can’t view full customer records
- Unique logins for every staff member, never a shared till password
- Multi-factor authentication on admin or back-office accounts where the system supports it
- PCI-compliant tokenisation, so full card numbers (PANs) are never stored on your system
- Regular software patching, active antivirus, and a POS network kept separate from guest Wi-Fi
Most small UK businesses that process personal data are legally required to register with the ICO, with fees split into three tiers: £52 for Tier 1, £78 for Tier 2, and £3,763 for Tier 3, correct as of February 2025. Most independent shops, cafés and restaurants sit in Tier 1 or Tier 2, and a direct debit shaves £5 off the annual cost. If you’re unsure which tier applies, the fee checker on GOV.UK takes about two minutes.
Practical processes: records, retention, and ICO fees
You don’t need a fifty-page compliance manual. A short record of processing activities (ROPA) that lists what data you collect, why, where it’s stored and who can access it is enough for most independent retailers and is genuinely useful evidence if the ICO ever asks questions. Some businesses under 250 staff qualify for a partial exemption from formal ROPA duties, but keeping one anyway helps you spot data leaks where a third-party POS integration is quietly holding onto more customer data than you realised.
For retention, a few sensible defaults:
- Transactional receipts: keep as long as your accounting and tax obligations require, then delete
- Loyalty scheme data: review annually and remove records for lapsed or inactive customers
- CCTV footage: short retention (often 30 days) unless it’s needed as evidence for a specific incident
Registering with the ICO and paying the correct fee tier isn’t optional for most trading businesses. It’s also one of the simplest boxes to tick, and skipping it is a common, entirely avoidable compliance gap.
If POS data is breached: your incident response checklist
Breaches happen, often through a lost device, a phishing email, or a misconfigured cloud setting. What matters is how fast you respond.
- Contain the breach immediately: isolate affected systems, change passwords, and preserve logs as evidence.
- Assess the risk to individuals. Ask whether the exposed data could cause harm, financial loss, or distress.
- Notify the ICO within 72 hours if the breach is likely to result in a risk to people’s rights and freedoms.
- Notify affected individuals directly if the risk is high, explaining what happened and what you’re doing about it.
- Record the incident, including what went wrong and what you’ve changed to stop it recurring.
The ICO’s guidance for small organisations is refreshingly practical here: most of what’s expected is common sense, not legal complexity.
When does a POS project need a DPIA?
A Data Protection Impact Assessment (DPIA) becomes necessary when your POS project involves systematic profiling, large-scale customer data processing, or CCTV that covers public areas beyond basic security monitoring. Adding a new loyalty analytics feature or rolling out facial recognition at checkout are classic triggers.
Even when a DPIA isn’t strictly required, running through the exercise is worthwhile:
- Describe the processing in plain terms
- Assess whether it’s necessary and proportionate
- Identify realistic risks to customers
- List mitigations and get sign-off from whoever manages data protection
This ties directly to the data protection by design and by default duty under Article 25 of the Data Protection Act 2018: building privacy in from the start, not bolting it on afterwards.
Making GDPR part of everyday POS operations
Compliance rarely fails because of one dramatic mistake. It usually erodes through small habits: a shared login, a receipt left on the counter, a loyalty export nobody remembered to delete. The fix isn’t a thick policy document. It’s folding checks into shift handovers and admin routines that already happen, and assigning one clear person to own subject access requests and system updates. Treat it as part of the job, not a separate project, and reference resources like our POS data migration guide when moving systems securely.
— Amir
How Switch-and-save helps you manage GDPR obligations at the till
Compliance shouldn’t mean choosing between a secure system and an affordable one. EPOS bundles for retail and hospitality businesses often include encrypted cloud storage, role-based access controls, and UK-based support knowledgeable about relevant data protection rules.
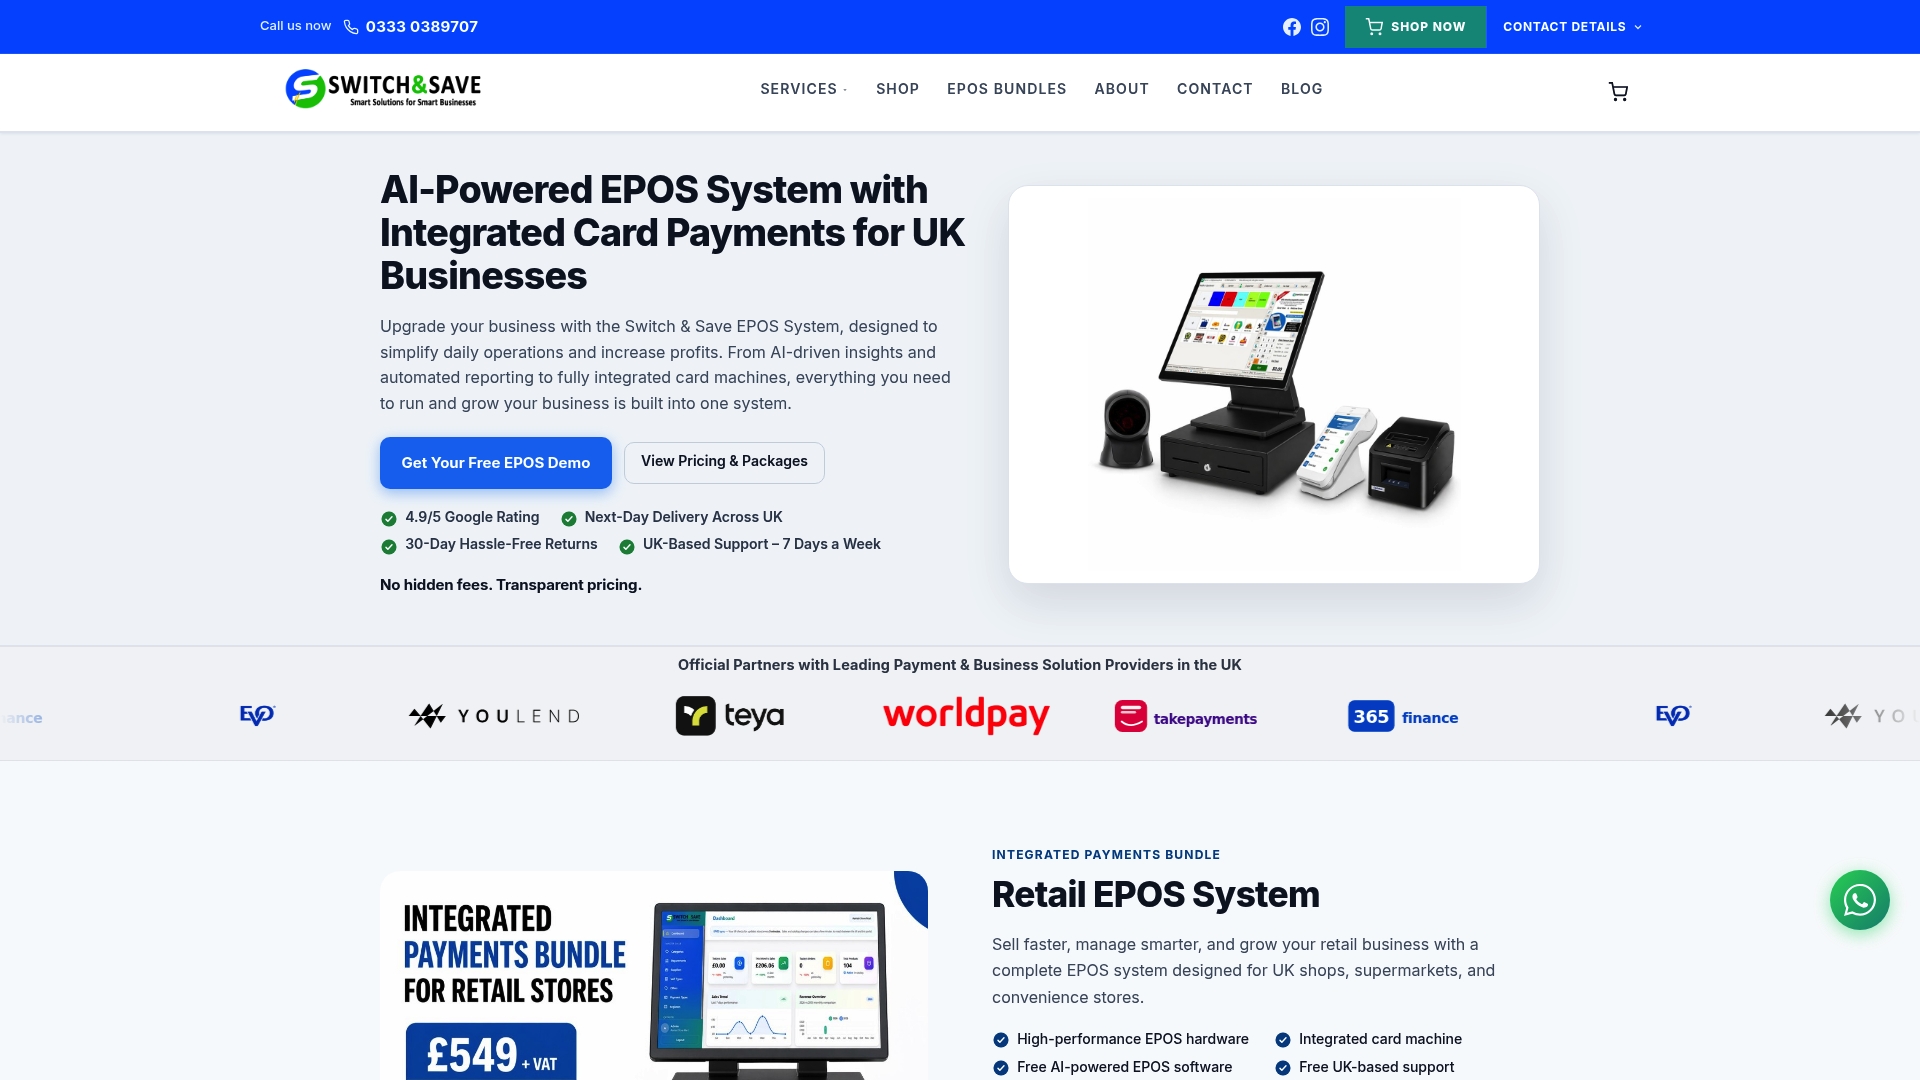
The Hospitality EPOS Bundle comes with AI-powered cloud software for £20 a month, and if you’re weighing up payments and card terminals together, the Integrated Payments Bundle combines EPOS software (£30 a month) with a certified card terminal so you’re never storing full card numbers on your own system. Migration from your current provider may be handled by UK-based teams, which can help mitigate risks of data loss during the switch.
One honest note: the legal decisions, your lawful basis, your retention periods, remain your responsibility as the business owner. Good hardware and software make compliance easier; they don’t replace the paperwork. If you’d like to see how it works in practice, browse the full range of EPOS bundles or book a free demo to ask questions specific to your shop or restaurant.
Sources
- Security principle under UK GDPR (guidance)
- Data protection by design and default (Data Protection Act 2018, section 57)
- Getting started with data protection (ICO)
FAQ
Does GDPR apply in the United Kingdom?
Yes. UK GDPR, alongside the Data Protection Act 2018, governs how businesses handle personal data across England, Scotland, Wales and Northern Ireland, and it’s enforced by the ICO.
What are the seven UK GDPR principles?
They are lawfulness, fairness and transparency; purpose limitation; data minimisation; accuracy; storage limitation; integrity and confidentiality (security); and accountability.
Does GDPR apply to small businesses?
Yes, GDPR applies regardless of business size, though some very small organisations qualify for partial exemptions from formal record-keeping, and most still need to register with the ICO and pay the relevant fee.
What is exempt from UK GDPR?
Purely personal or household activity is exempt, along with some limited processing tied to law enforcement or national security. Ordinary retail and hospitality transactions are not exempt.
Does Switch-and-save offer GDPR-ready POS systems?
Switch-and-save’s EPOS bundles include encrypted cloud storage, role-based access and PCI-compliant card handling, features that support your compliance efforts. Current pricing is available on the Hospitality EPOS Bundle and product bundle pages.